Import Data from CrowdStrike Falcon Spotlight
Import CrowdStrike Falcon Spotlight findings into Mondoo alongside your own scan results.
Mondoo can import data from CrowdStrike Falcon Spotlight and combine it with your Mondoo findings. The unified view gives you Mondoo's security visualization, prioritization, and ticketing on top of CrowdStrike exposure data.
Prerequisites
- Editor or Owner access to the Mondoo space
- Administrator access to a CrowdStrike Falcon account
- Falcon Spotlight exposure management enabled
- Falcon Discover enabled (optional, lets Mondoo pull software inventory)
Create a CrowdStrike Falcon API client
Mondoo authenticates with a CrowdStrike API client. To learn more, see CrowdStrike OAuth2-Based APIs in the Falcon documentation.
-
Log into the Falcon console as a Falcon Administrator.
-
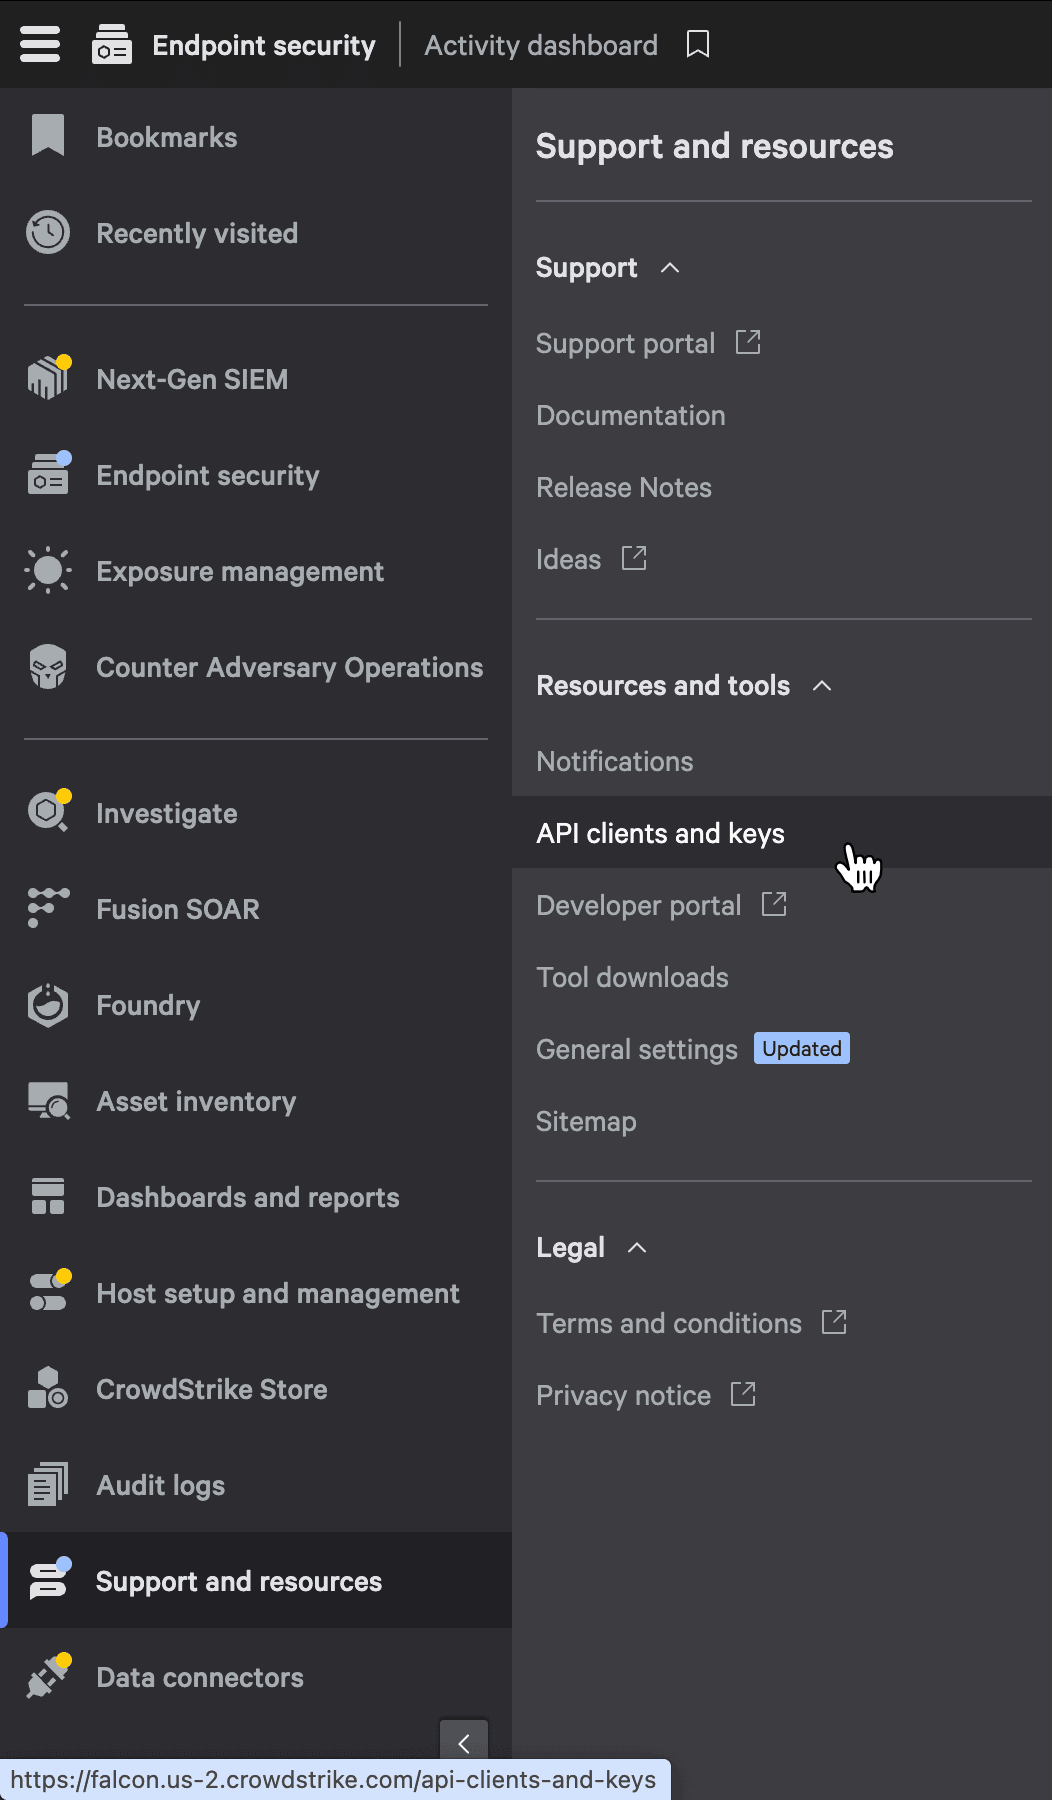
In the left navigation, select Support and resources > API clients and keys.
-
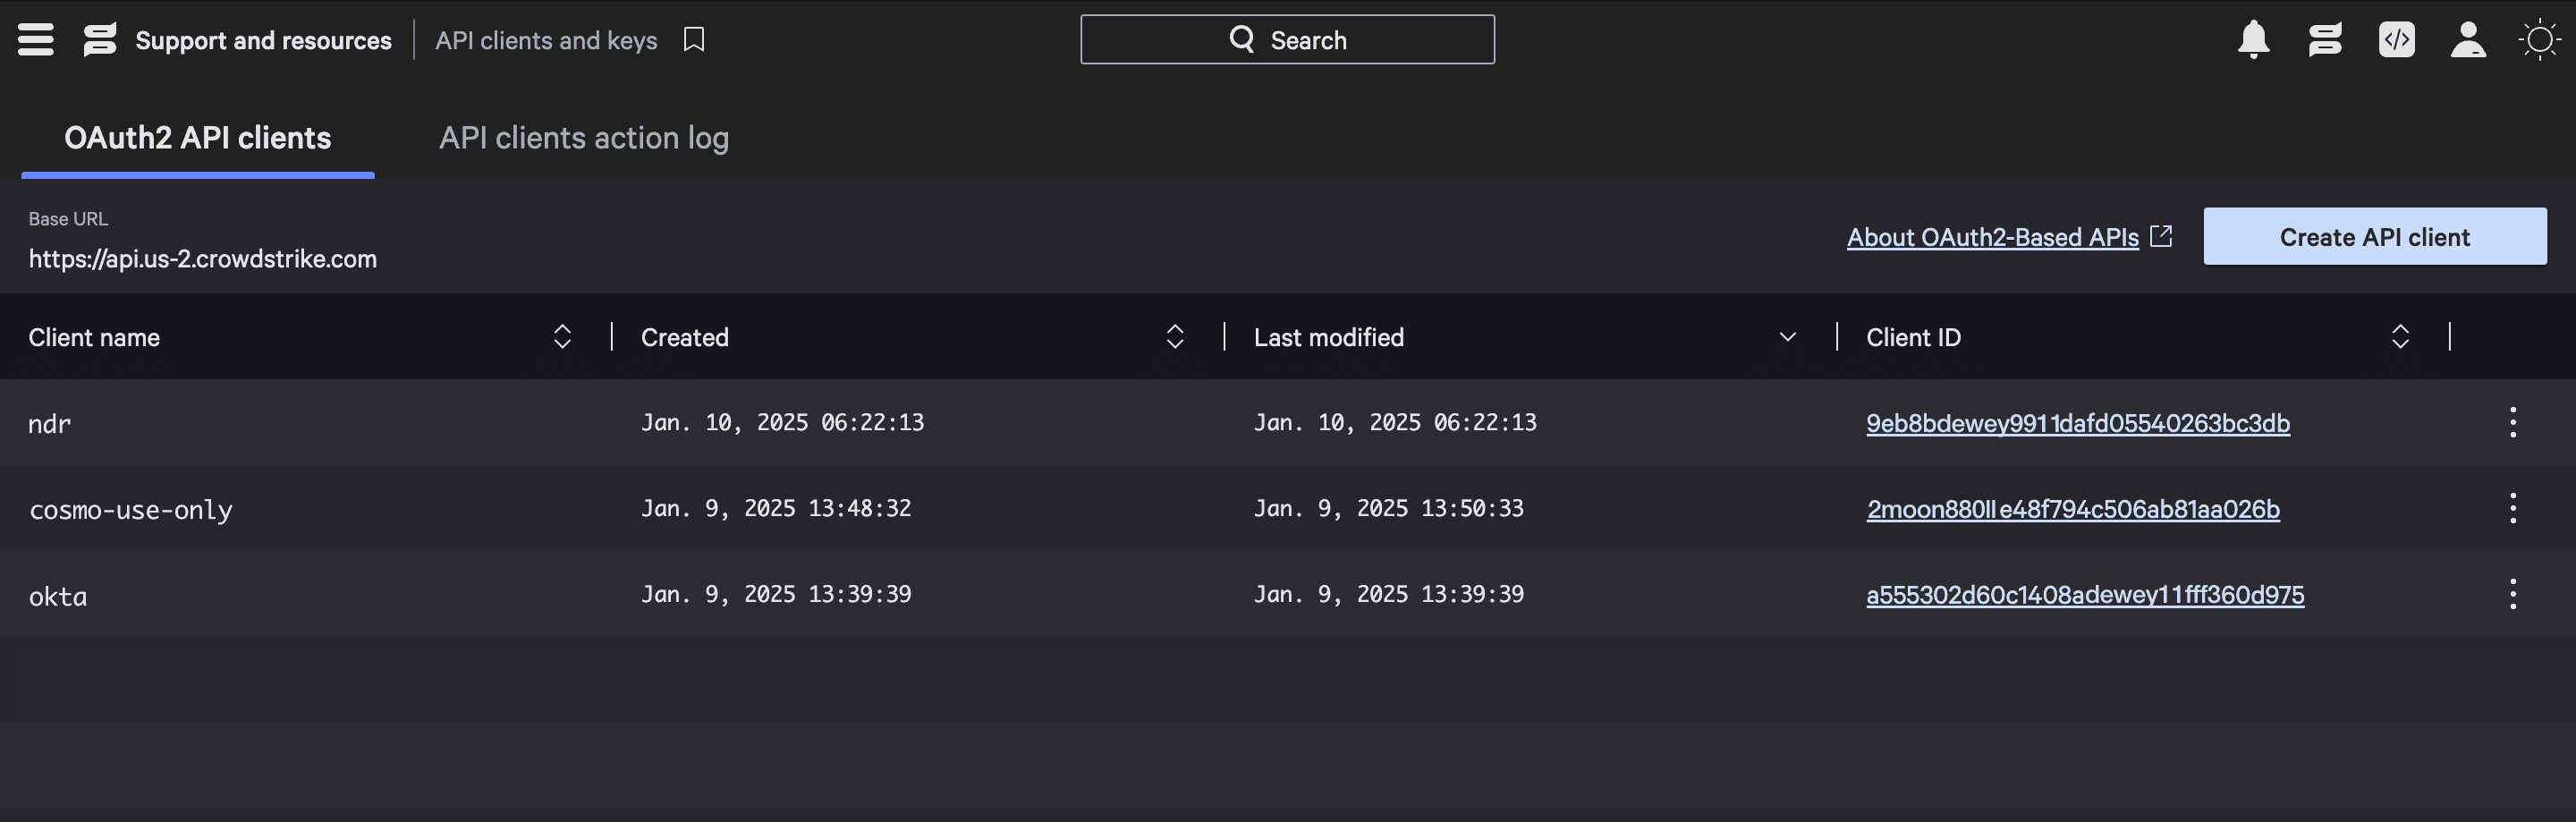
Select Create API client.
-
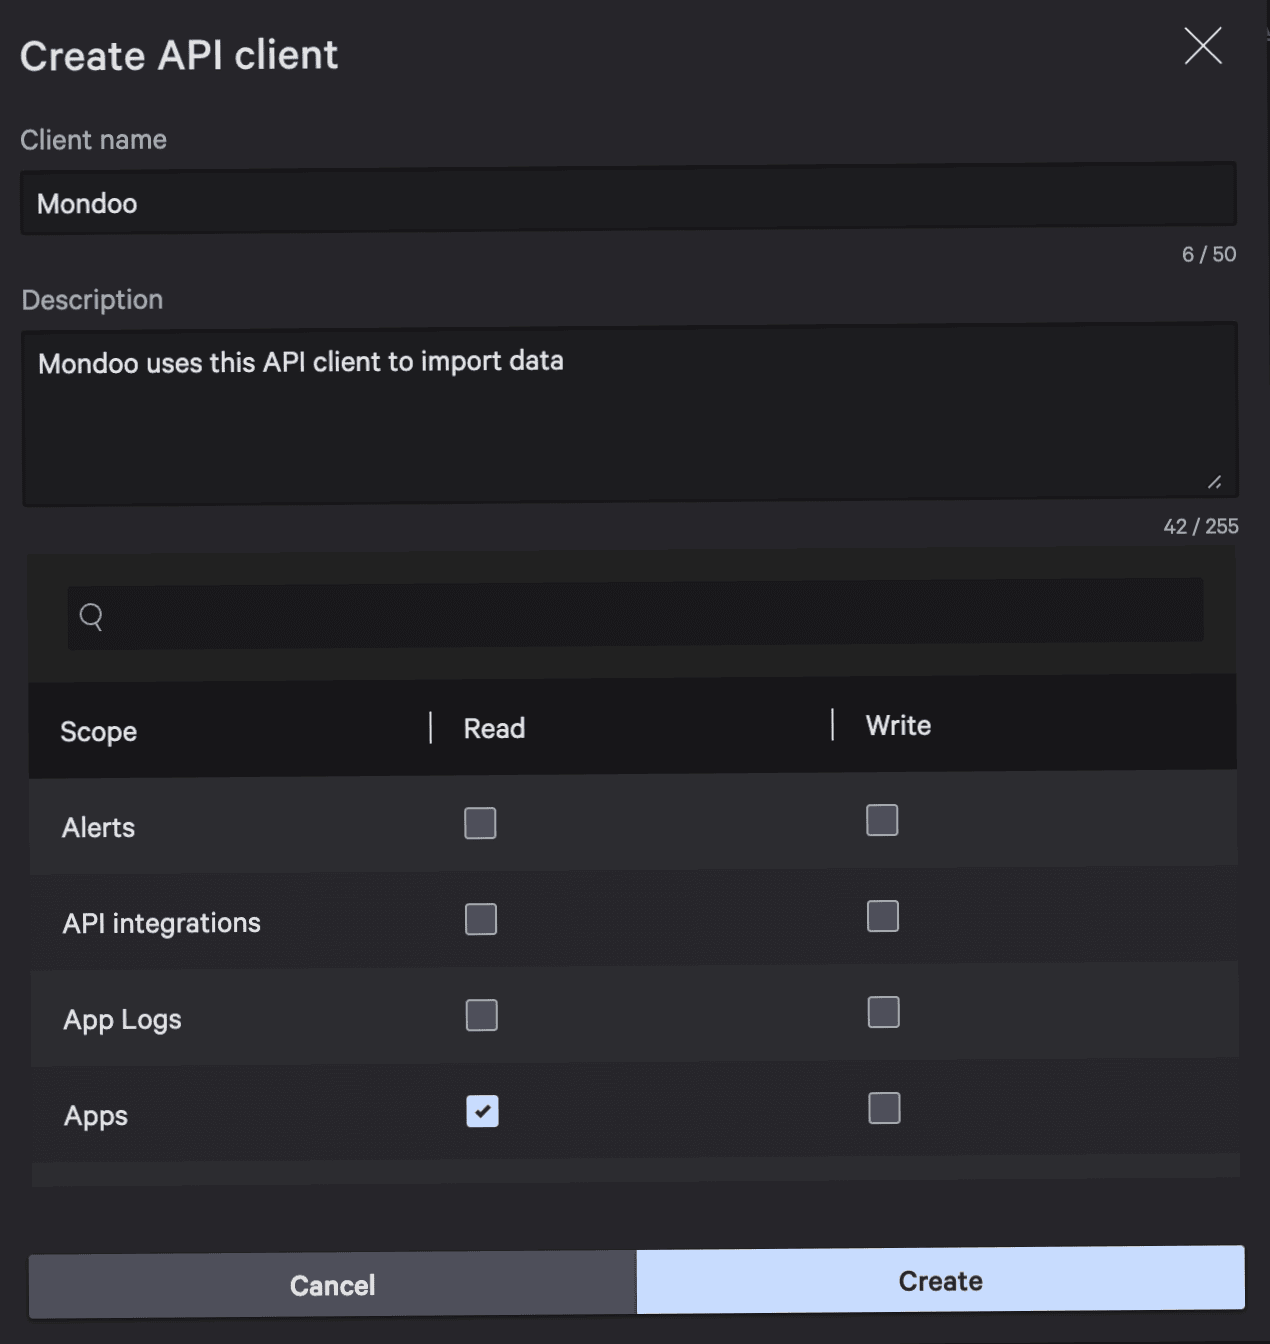
Give the client a name that identifies it as Mondoo's.
-
In the Scopes table, check the Read column for each of:
- Apps
- Detections
- Device content
- Device control policies
- Hosts
- Assets (only if Falcon Discover is enabled)
- Vulnerabilities
- Alerts and Quarantined Files (only if you want to import threats and malware)
-
Select Create.
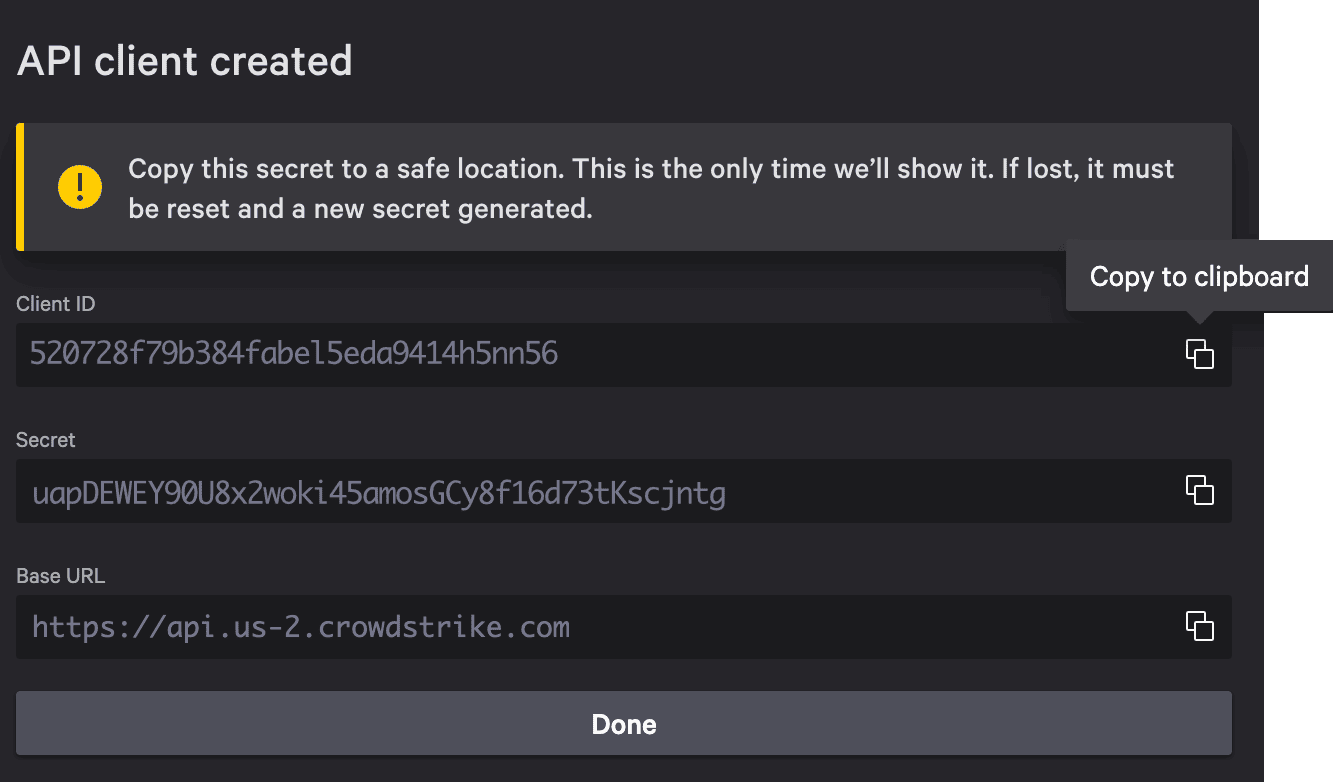
Falcon shows the client ID, secret, and base URL Mondoo needs. Keep the page open for the next section.
Add a CrowdStrike Falcon integration
In the Mondoo App, navigate to the space where you want to add the integration. In the side navigation bar, select Integrations. In the top right, select INSTALL. On the Install Integration page, find the integration you want by browsing a category or searching by name:
-
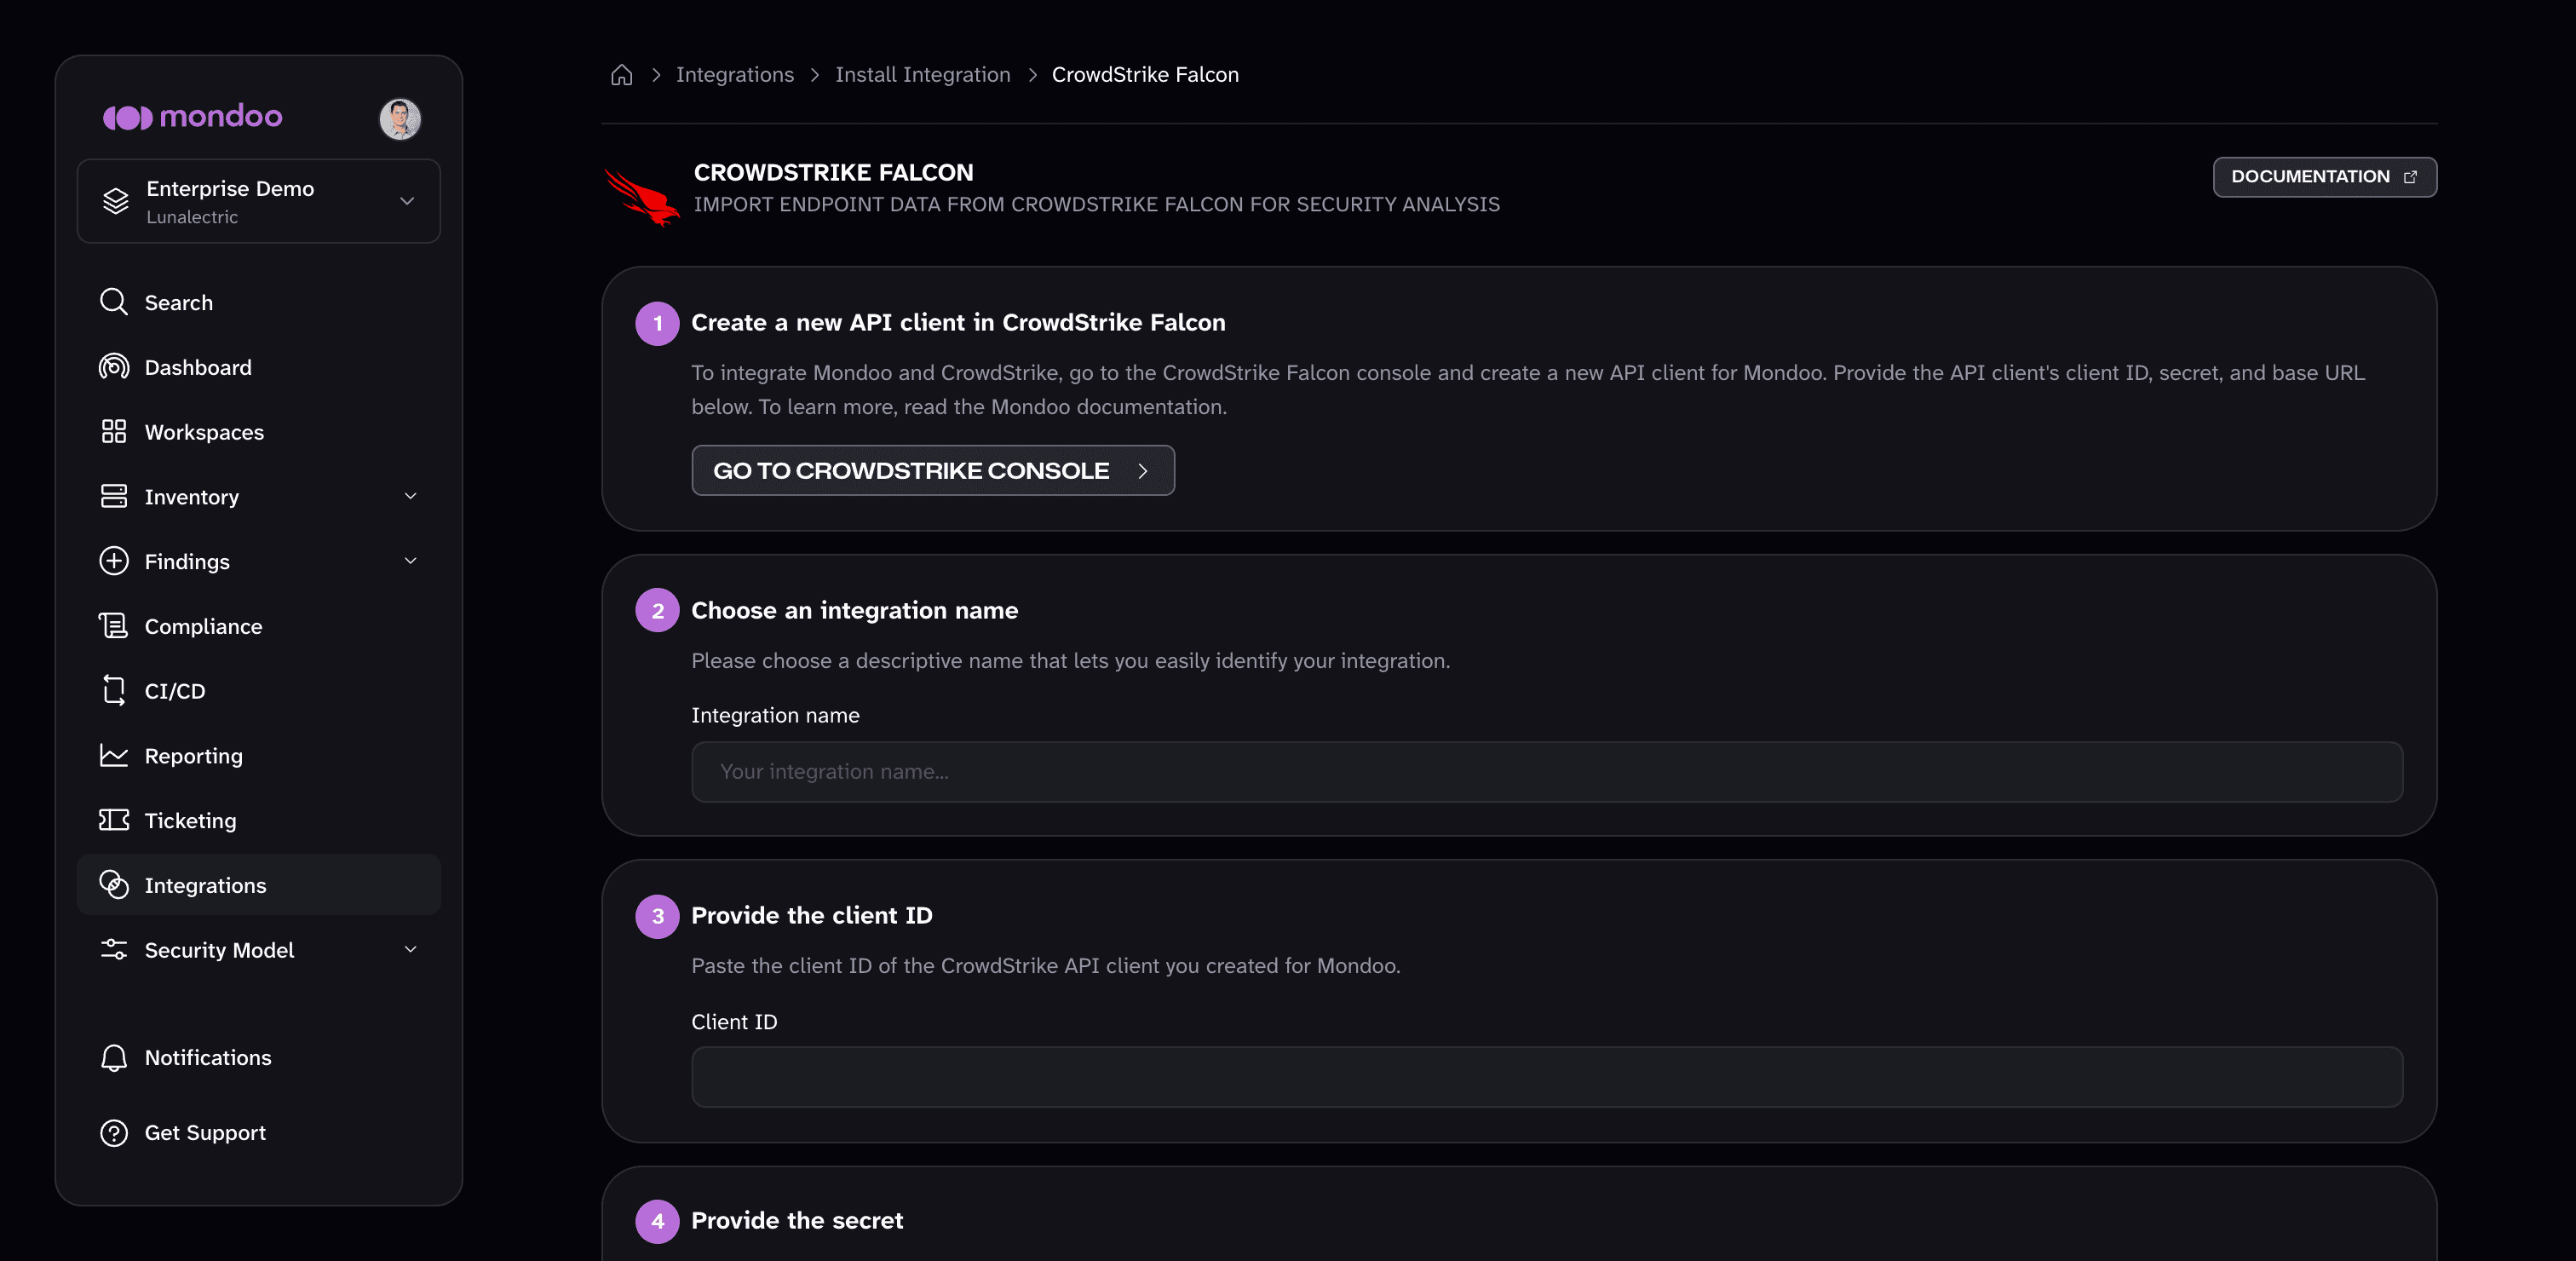
Under Third-Party Data, select CrowdStrike Falcon.
-
In Choose an integration name, enter a name for the integration.
-
Fill in these values from the API client you just created:
- Provide the client ID
- Provide the secret
- Provide the Cloud URL (the base URL Falcon shows for the API client, for example
https://api.us-2.crowdstrike.com)
-
Under Configure member CID usage, leave Export data from a specific member CID disabled unless you manage multiple CrowdStrike CIDs. To learn when this matters, see Multiple CrowdStrike CIDs below.
-
Under Configure preferences, choose how Mondoo handles the imported data:
- Create new assets for unique detections (off by default): add an asset for each device CrowdStrike reports that doesn't match an existing asset in the space.
- Enrich findings with Mondoo (on by default): run Mondoo's vulnerability database against the data CrowdStrike reports so findings include remediation guidance.
- Import threats and malware (off by default): import Falcon endpoint alerts and quarantined files as threat and malware findings. This option requires two more Read scopes on the API client: Alerts and Quarantined Files.
-
Select CREATE INTEGRATION.
Multiple CrowdStrike CIDs
If you're an administrator who manages multiple CrowdStrike CIDs (for example, an MSP handling several customers), one API client can access multiple CIDs. Mondoo lets you scope the integration to one CID at a time.
To find the CID:
-
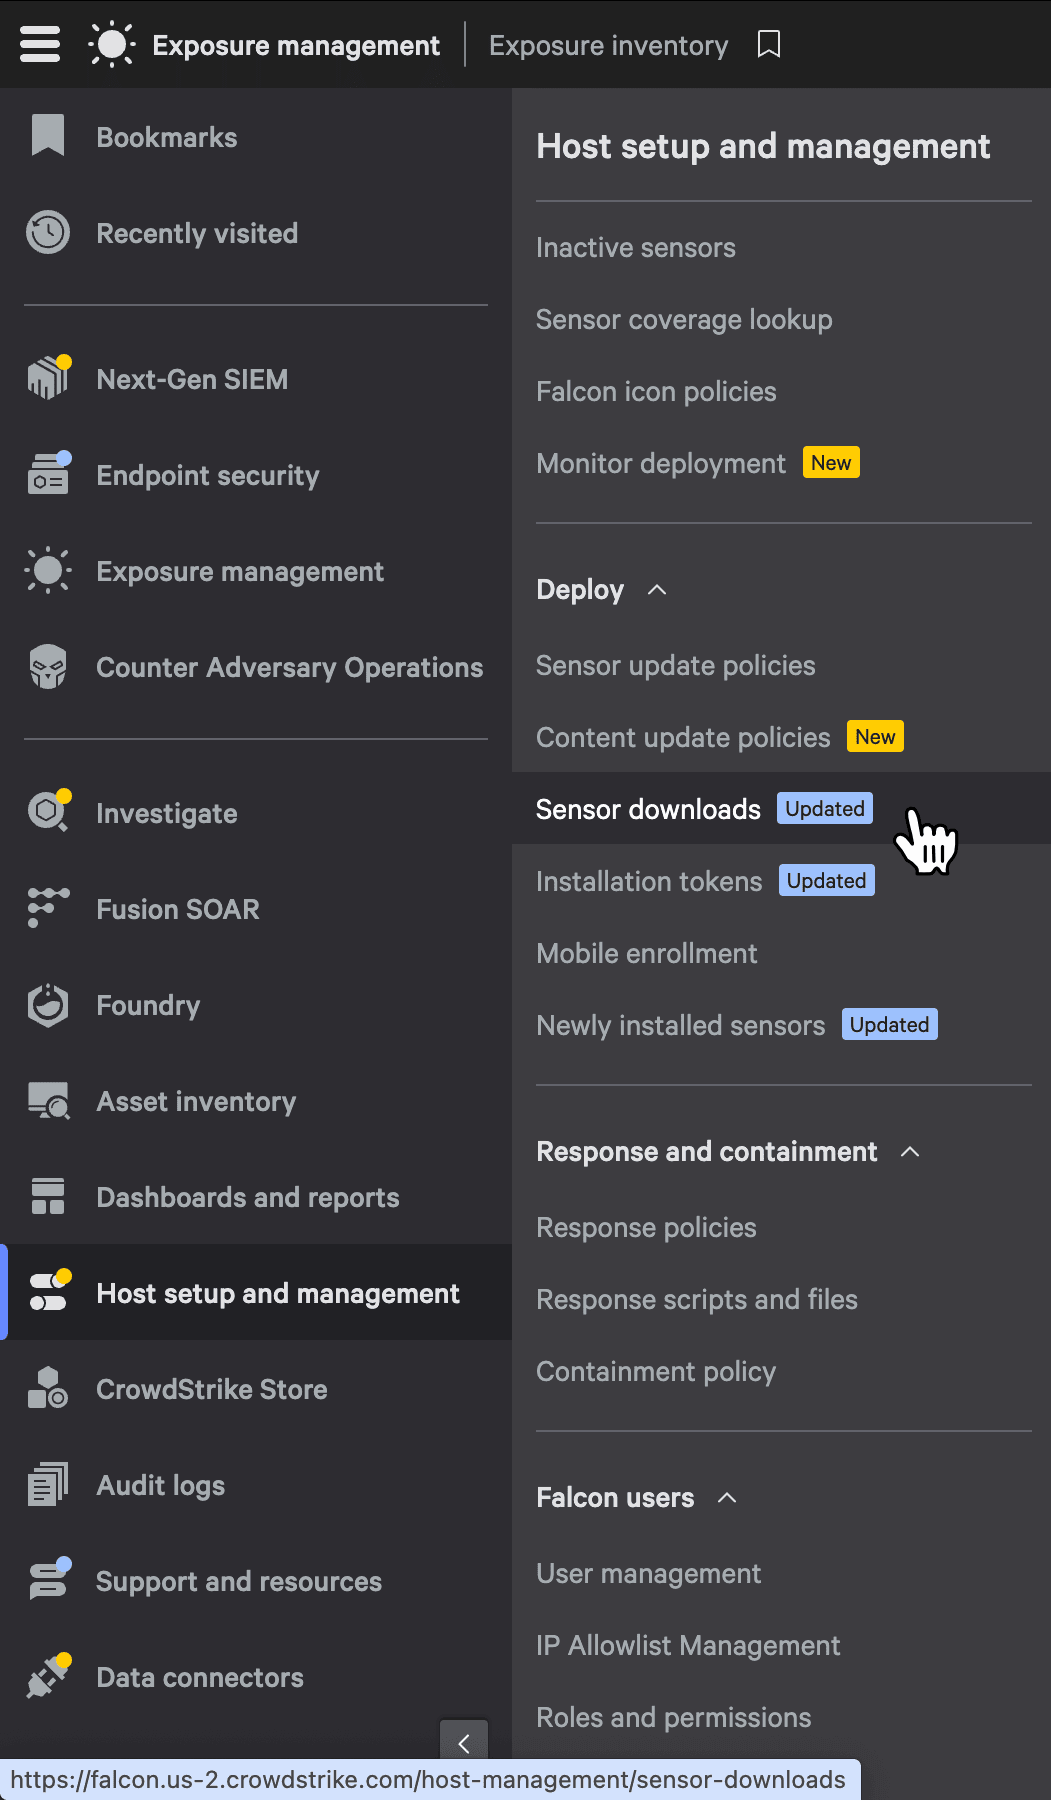
In the Falcon console, go to Host setup and management > Deploy > Sensor downloads.
-
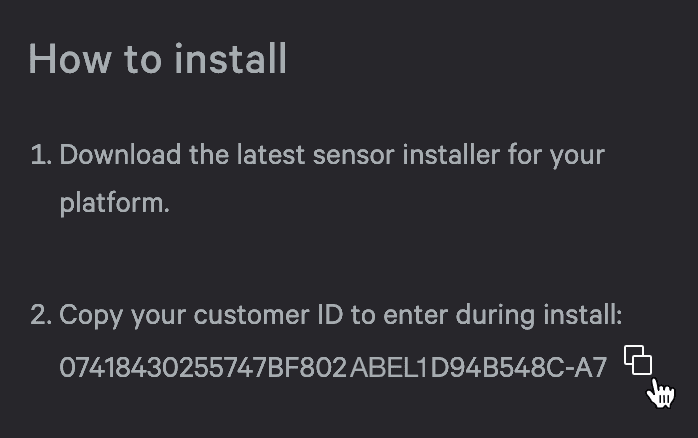
Under HOW TO INSTALL, select the copy icon beside the Customer ID. Paste this value in Mondoo's Provide the member CID box and enable the toggle.
Manage this integration
To open an existing integration, navigate to the space, select Integrations in the side navigation, choose the integration type, then select the integration.
The integration detail page shows the integration's status, configuration, import details, and recent activity. From there, you can:
- Trigger an immediate import. Select RUN.
- Edit settings. Select the edit (pencil) icon.
- Remove the integration. Select the trash can icon and confirm.
After you connect
Once the import is running, your CrowdStrike findings appear in Mondoo alongside its own. Assess and improve your security to review and prioritize them.