
Free guide
See how your security program stacks up
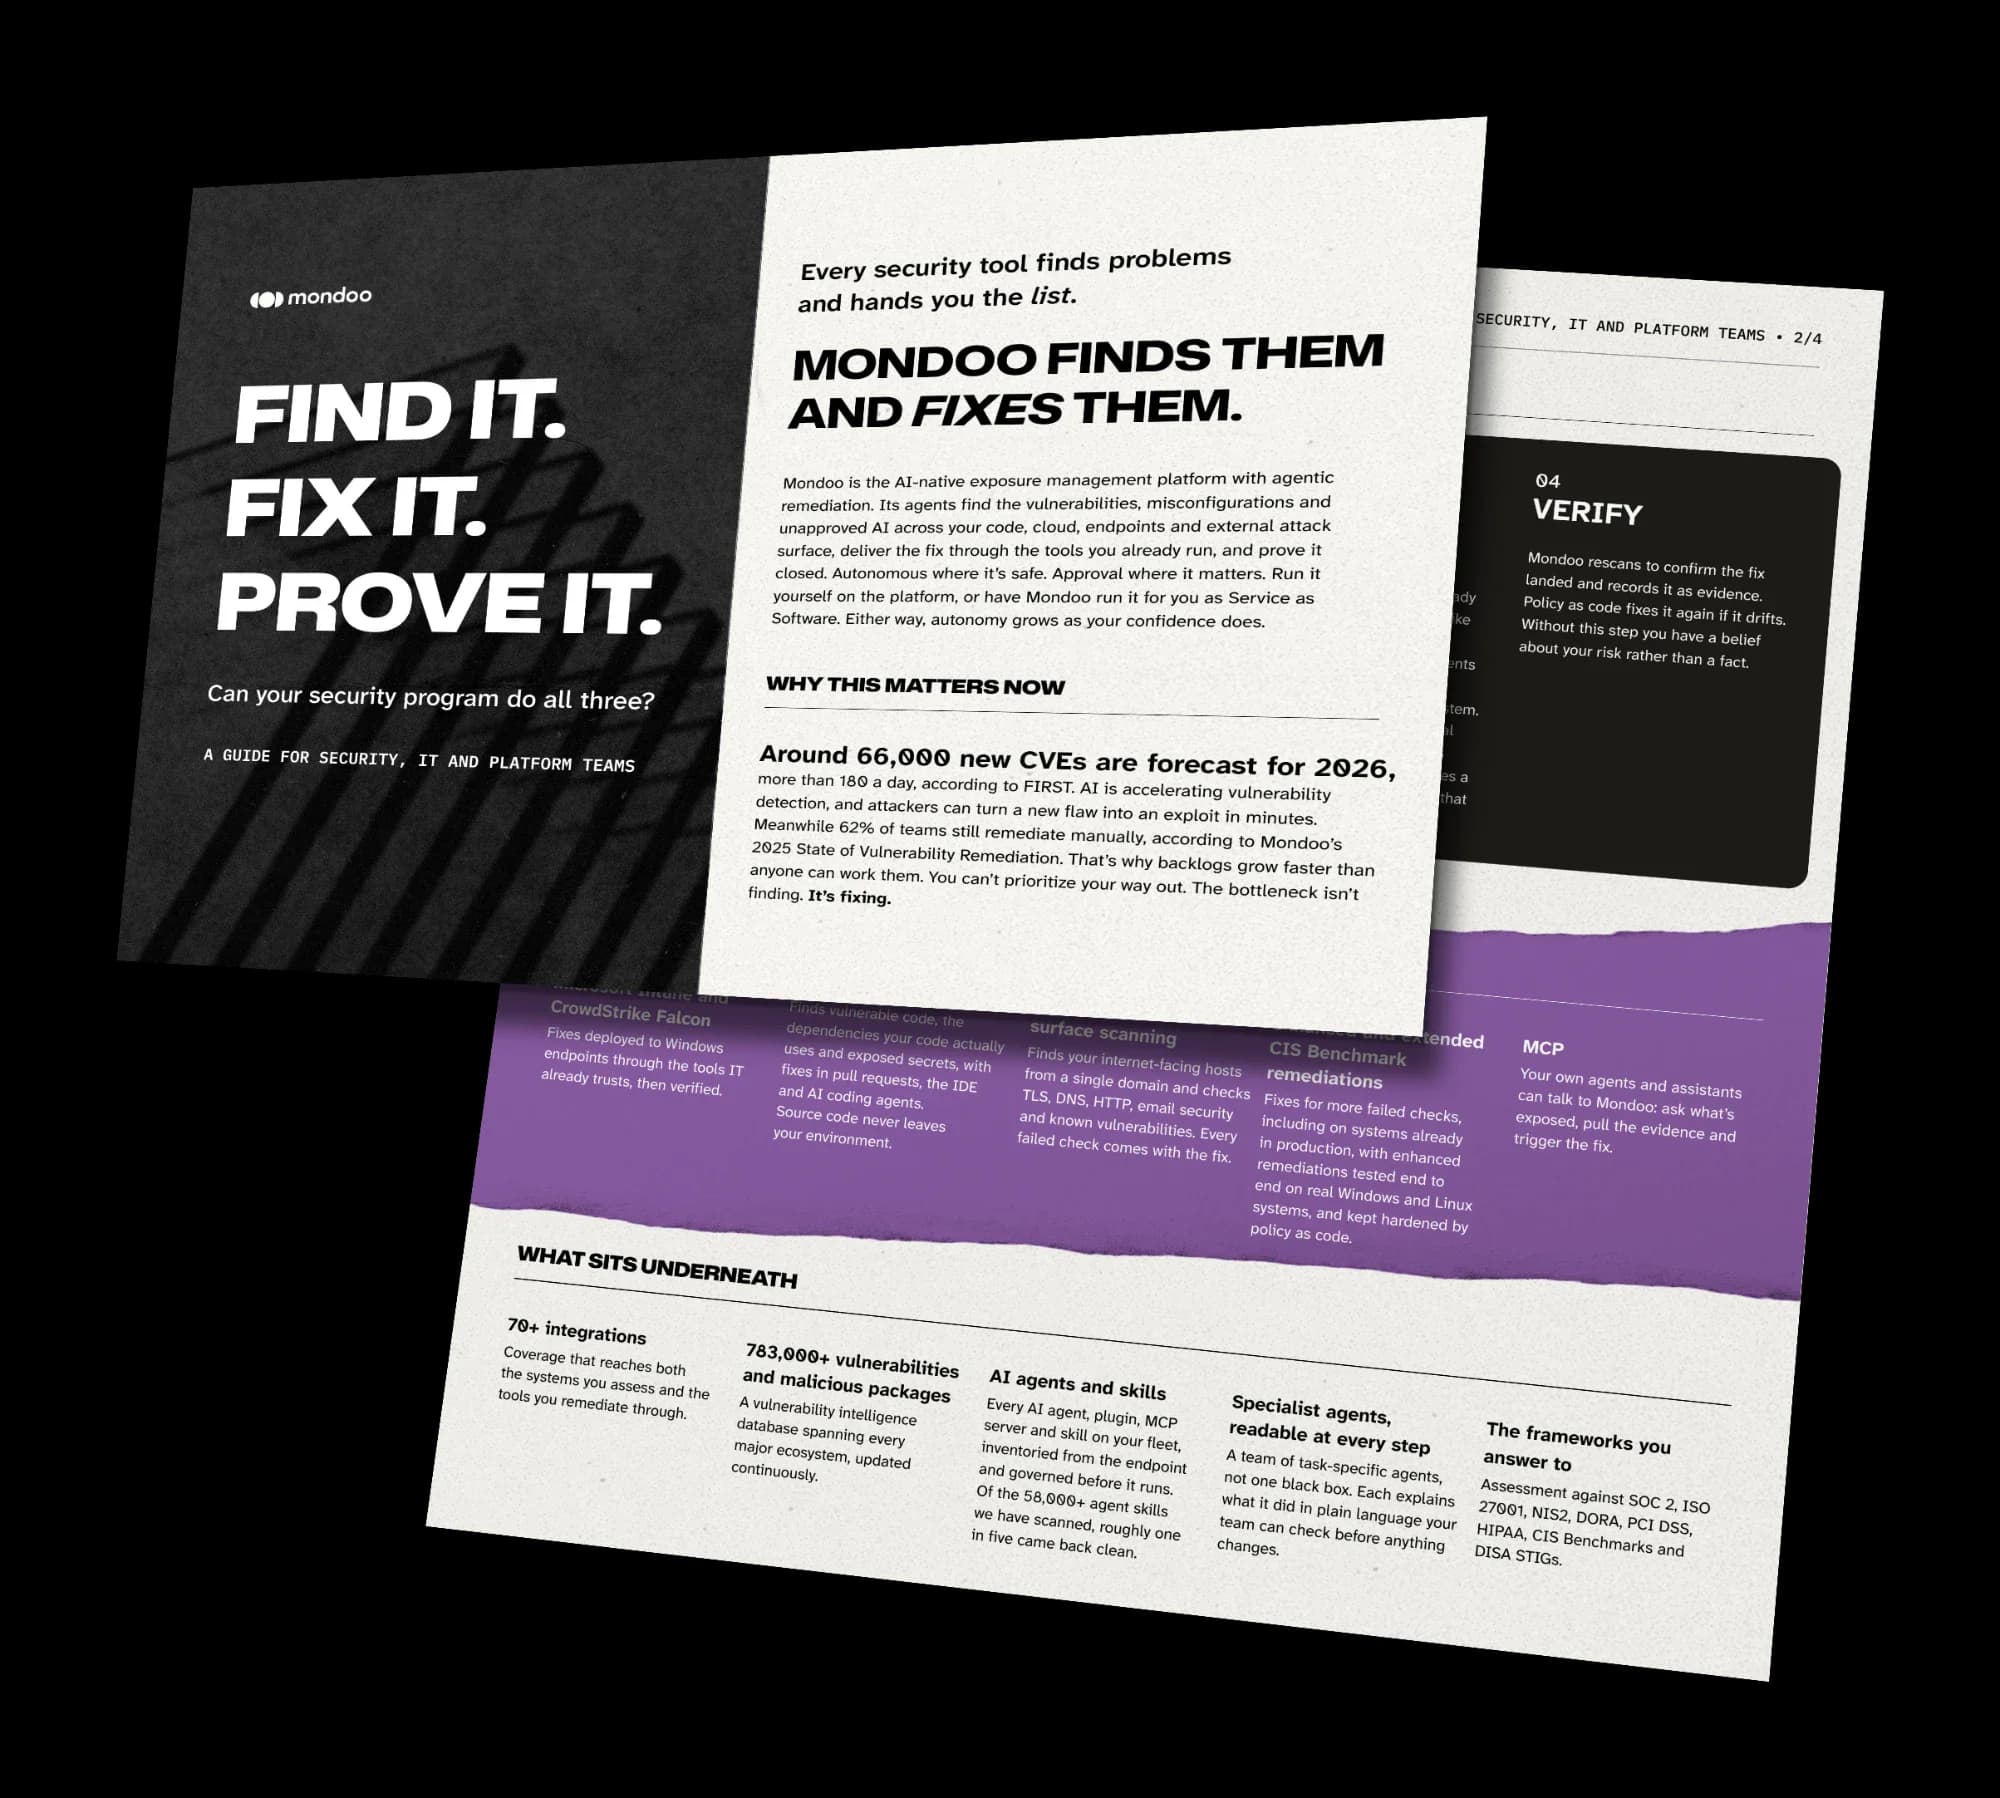
Find it. Fix it. Prove it. What it takes to close findings, how Mondoo does it, and a nine-question checklist to tell whether your own program closes the loop.
Three reasons to open it
- Why 66,000 new CVEs this year mean you can't prioritize your way out, and why the bottleneck is fixing
- How to go from finding to verified fix: autonomously where it's safe, with approval where it matters
- The questions to ask before you buy another scanner
What closing the loop produces
- Remediations performed
- 5M+By Mondoo's agents and experts, to date.
- Customers worldwide
- 300+From enterprises to managed security service providers.
- Evidence of every fix
- On demandWhat was found, fixed, approved and verified, without the scramble before an audit.
Telecoms, automotive, banking, manufacturing and travel. Companies running estates from AIX to AWS use Mondoo to find what is exposed, fix it, and produce the evidence, without adding headcount.
Read the case studies



Certifications
- SOC 2 Type II certified
- ISO 27001 certified
- CIS SecureSuite member
- GDPR compliant
One platform across everything you run
Nobody is short of findings. Scanners produce lists, and the fixing becomes your problem. Mondoo runs the whole loop instead: we find what is exposed, work out what actually matters, ship the fix, and prove it closed. Around 66,000 new CVEs are forecast for 2026, more than 180 a day (FIRST), and 62% of teams still remediate manually (Mondoo 2025 State of Vulnerability Remediation), which is why backlogs grow. Every fix is re-checked and held closed, so the evidence auditors, insurers and customers ask for builds itself as the work happens.
01 — Across Your Attack Surface
Detect
Continuous assessment across code, cloud, endpoints, infrastructure, AI and your external attack surface. No new agents to roll out, so coverage starts on day one instead of after a deployment project.
02 — Rank by Exploitability
Prioritize
Ranked by business impact and real exploitability, not severity score alone, so the queue reflects what an attacker could actually use.
03 — Deliver the Fix
Ship
Fixes land through the tools your team already operates: Microsoft Intune and CrowdStrike Falcon, GitHub pull requests, Ansible, Terraform and your ticketing system. Autonomous where it's safe, approval where it matters, and every action is logged.
04 — Confirm It Is Closed
Verify
Fixes are re-checked and held closed, and policy as code fixes them again if they drift, with the evidence ready for auditors, insurers and customers who now ask for it.
- Surfaces
- Code, cloud, on-premises, endpoints, SaaS, network devices, containers, the software supply chain, your AI estate and your external attack surface.
- Works with
- AWS
 Azure
 Google Cloud
 Kubernetes
 Microsoft Intune
 CrowdStrike Falcon
 Ansible
 Terraform
- GitHub
 Jira
70+ integrations, and the tools your team already runs on both ends of it.
- We assess your estate against
 SOC 2
 ISO 27001
 NIS2
 DORA
 PCI DSS
 HIPAA
 CIS Benchmarks
- DISA STIGs
What we cover
One platform across every surface, and AI findings land in the same queue as your CVEs rather than in a separate console.
- Vulnerability IntelligenceSearch 783,000+ known vulnerabilities and malicious packages across every major ecosystem.
- Shadow AIEvery AI agent, plugin and MCP server on your fleet, inventoried from the endpoint and governed before it runs.
- AI Skills CheckFree and agent-agnostic. Of the 58,000+ agent skills we have scanned, roughly one in five came back clean.
- Exposure ManagementContinuous assessment across your estate, prioritized by real exploitability rather than CVSS alone.
- Agentic Vulnerability ManagementThe remediation engine that ships and verifies the fix inside the loop.
- PlatformThe engine underneath: policy as code, continuous assessment, and evidence that builds itself.
- Managed ServiceHave Mondoo run the entire loop for you as an outcome.
- Agentic RemediationFixes deployed, verified and kept fixed: autonomously where it's safe, with approval where it matters.
- CIS RemediationFix failed CIS Benchmark controls on running systems, and keep them fixed.
- Vulnerability PrioritizationFive risk dimensions, so the fixes that remove the most risk come first.
- MCP ServerMake every agent you run security-aware, and secure the MCP servers your teams use.
Vulnerabilities. Misconfigurations. Shadow AI.
Found, fixed, and proven closed.
Mondoo is the AI-native exposure management platform with agentic remediation: it finds what is exposed across everything you run, fixes it, and proves it closed.
What changes when the loop closes
- Your backlog shrinks instead of growing.
- Fixes ship through the tools you already have. Nothing new to deploy.
- Audit evidence builds itself as the work happens.
- Fixes run autonomously where it's safe, with your approval where it matters.
What this looks like in practice
Deutsche Telekom
350,000+
“The speed and accuracy of Mondoo's platform, combined with its deep insights into IT architecture, enables customers to quickly remediate issues and significantly reduce CVEs and policy violations.”
European travel group
6 people
Around 1,000 assets from AIX to AWS under continuous assessment, with audit evidence produced in three to four days instead of months.
Campminder
50%
Four separate tools retired, PCI DSS achieved, and four to five times less manual work for a team that stayed the same size.
Most teams start with an assessment. We map what is exposed in your environment and show what closing the loop would look like, before anything changes.
Fix Now. Fix Forever.